homelab
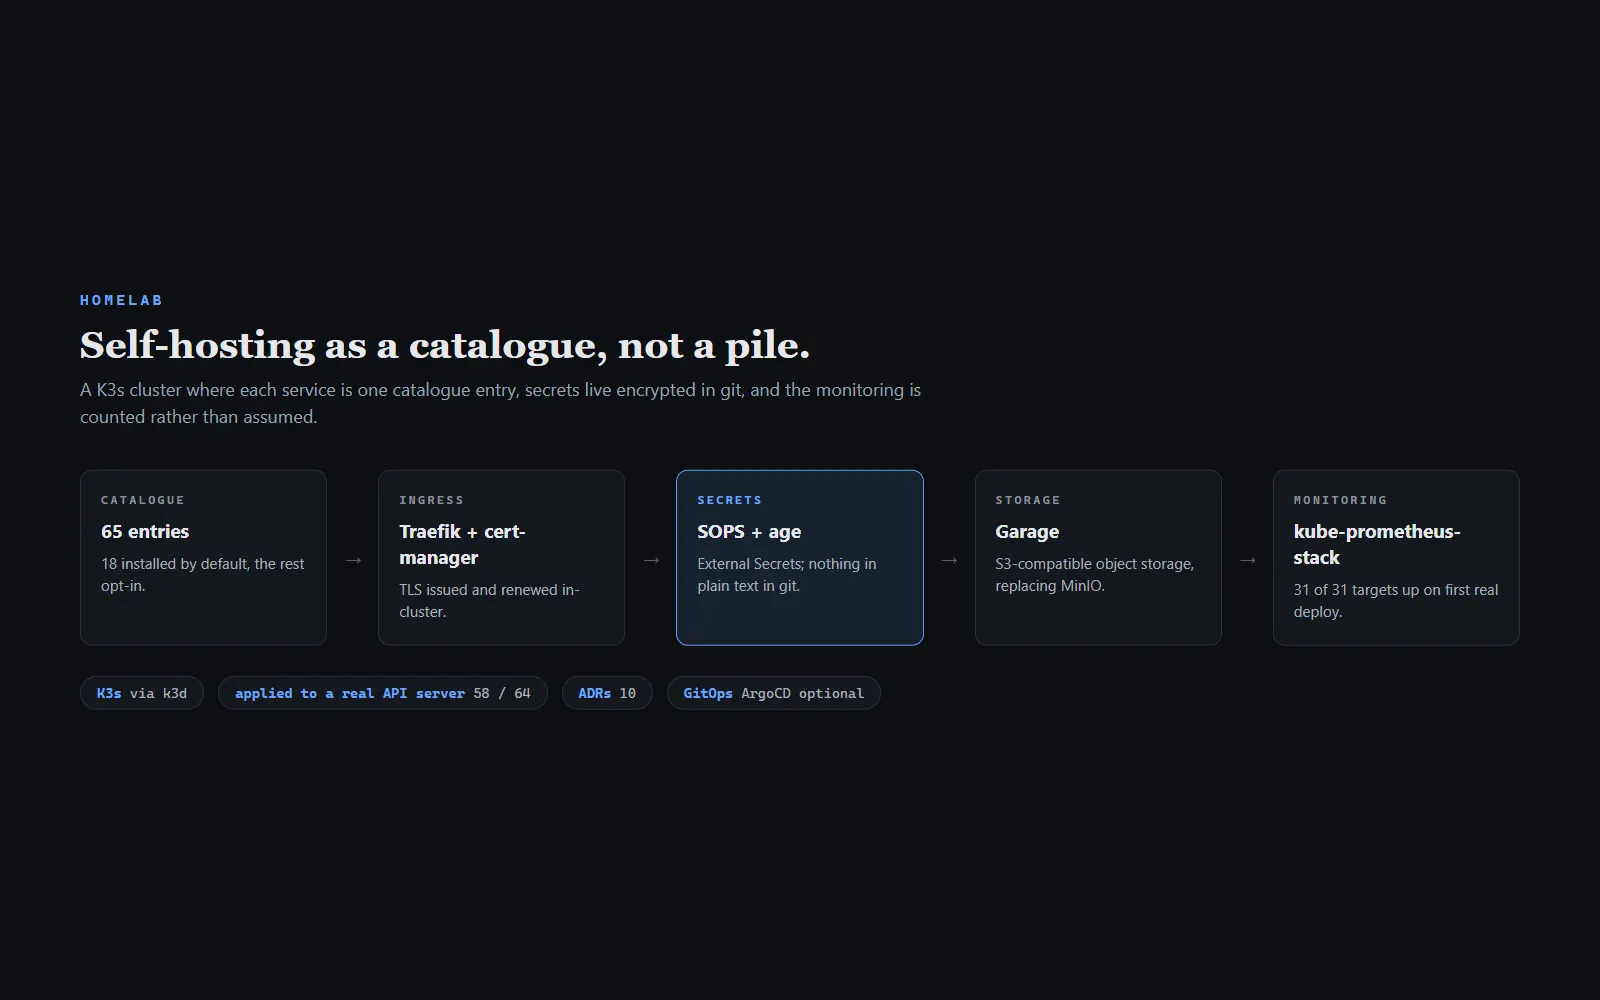
The second version of my homelab: a K3s cluster with a declarative service catalogue, TLS from cert-manager, secrets encrypted in git, and a Prometheus stack watching all of it. It replaced a Raspberry Pi running Docker Compose.
The constraint
pi-lab answered whether one Raspberry Pi could carry a homelab, and then hit the limits of Compose: every service its own snowflake, secrets in env files, and no way to say which services should exist without reading every directory.
The approach
Describe each service once in a catalogue, choose what is installed per environment, and let the cluster converge. Traefik and cert-manager handle ingress and TLS, External Secrets with SOPS and age keep secrets encrypted in git, and kube-prometheus-stack watches everything. ArgoCD is optional.
- 1Catalogue first
Refactored the service list into a catalogue so adding a service is one entry, and choosing what runs is configuration.
- 2Test against a real API server
Applied the manifests to a real Kubernetes API server, which catches failures that schema linting passes.
- 3Deploy, then measure
Counted Prometheus targets after the first real deploy rather than assuming the monitoring was wired.
Outcomes
- A 65-entry service catalogue: 18 installed by default, the rest opt-in
- 58 of 64 manifests applied cleanly to a real API server, not just linted
- 31 of 31 Prometheus targets up on the first real deploy
- Garage replaced MinIO for object storage
Rebuilt a self-hosted homelab as a K3s cluster with a declarative service catalogue, cert-manager TLS, SOPS-encrypted secrets and a Prometheus stack.
Related projects
- Read
Cocoon
A privacy-first Chrome extension that lowers sensory load online: it softens algorithmic feeds, reduces motion, and keeps a grounding exercise one click away. No accounts, no analytics, nothing leaves the device.
- Read
unlinkd
Get yourself removed from the internet — and keep the proof. A local-first, fully encrypted workspace for data-broker removal requests and the tamper-evident paper trail a GDPR or CCPA escalation actually needs.
- Read
FraudStream
A production-grade streaming pipeline that scores financial transactions for fraud in milliseconds rather than hours, built on Kafka, Spark Structured Streaming, and a Snowflake medallion warehouse.